National Post UK
Digital Infrastructure Under Siege as AI-Discovered PHP Flaw Sparks Global Crisis

A critical vulnerability in the backbone of the internet has triggered a cascade of malicious activity. As British autho

The National Post

HomeTechnology
Technology

Digital Infrastructure Under Siege as AI-Discovered PHP Flaw Sparks Global Crisis

A critical vulnerability in the backbone of the internet has triggered a cascade of malicious activity. As British authorities scramble to assess the damage, the incident serves as a sobering reminder of the volatility introduced by automated threat discovery.

JM

Jack Morrison

Technology Editor

Published 23 October 2026·about 3 hours ago 3 min read
Text
Share

The Automation Paradox The global internet ecosystem is currently navigating its most precarious security challenge in years following the revelation of a critical vulnerability within PHP, the pervasive programming language that acts as the scaffolding for nearly 75 percent of the world’s websites. The flaw, which has already facilitated millions of automated cyberattack attempts, was not uncovered by human researchers but by an artificial intelligence system designed to stress-test software architecture. This development marks a watershed moment in the field of cybersecurity, illustrating the dual-use nature of machine learning: the same tools capable of fortifying our digital borders are now serving as the catalyst for systemic instability.

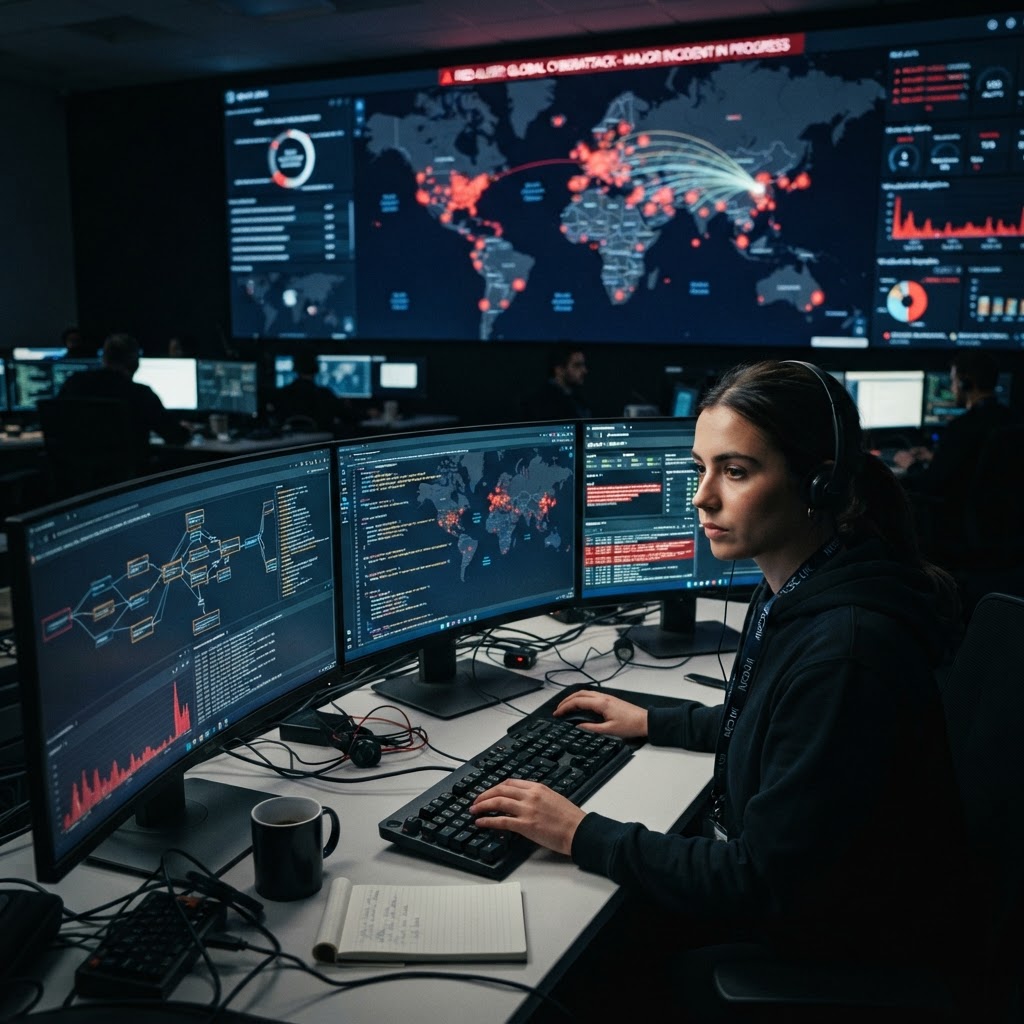
A Breach of Protocol The situation escalated rapidly after technical specifics of the vulnerability were leaked across social media platforms, bypassing the standard coordinated disclosure process. By the time the PHP Foundation—the non-profit organisation responsible for maintaining the language—prepared a patch, the digital floodgates had already been breached. For IT departments across the United Kingdom, the last forty-eight hours have been a period of relentless remediation, as organisations from the public sector to high-street retailers rush to identify legacy systems that rely on unpatched versions of the code.

Governmental Oversight and Response The UK’s National Cyber Security Centre (NCSC) has confirmed it is actively working with international intelligence partners to gauge the extent of the infiltration. While the NCSC has stopped short of providing a detailed audit of British exposure, sources within Whitehall suggest that critical infrastructure providers are being placed under heightened observation. The risk is not merely confined to data theft; the nature of this particular vulnerability allows for remote code execution, effectively granting attackers the ability to commandeer servers at will. This represents a significant escalation from simple data scraping, posing a threat to the operational continuity of essential services.

Expert Perspectives Dr. Elena Vance, a lead analyst at the Institute for Digital Security, views this incident as a fundamental shift in the cyber-threat landscape. The velocity at which the exploit moved from a laboratory curiosity to a weaponised tool is unprecedented. In the past, attackers required weeks to reverse-engineer a vulnerability once a patch was released. Here, the AI identified the weakness, the exploit was weaponised by bad actors before a fix existed, and the resulting payload was distributed globally within a matter of hours. We are witnessing the first true example of a machine-speed arms race.

The Broader Implications The vulnerability has forced a reckoning among major technology corporations. Amazon and other cloud-infrastructure giants have been forced to deploy emergency firmware updates to their managed hosting environments, providing a buffer for millions of smaller businesses that may lack the technical capacity to self-remediate. Yet, for thousands of legacy websites that lack active maintenance, the danger remains acute. As the dust settles, the conversation in Westminster and Brussels is expected to shift toward the regulation of AI-driven vulnerability research. Policymakers are faced with a difficult dilemma: how to incentivise the positive innovation brought by machine learning while mitigating the catastrophic risks posed by its misuse in the hands of malicious actors.

TopicsCybersecurityPHPArtificial IntelligenceNCSCTech NewsData Protection
Share

About the Author

JM

Jack Morrison

Technology Editor

Jack Morrison reports for National Post UK with a focus on rigorous analysis and authoritative journalism — a trusted voice across British public life.

Reader Discussion · 9

Subscribers can join the conversation.

SUBSCRIBE TO COMMENT →
E
Elena Gregory23 Oct

This just goes to show why we need to move away from legacy codebases that have been patched and re-patched for decades. We really should be investing in more modern, memory-safe languages to avoid these recurring nightmares.

M
Marcus Thorne23 Oct

I am not entirely convinced that the scale of the threat is as catastrophic as the headlines suggest. While PHP vulnerabilities are certainly problematic, the majority of enterprise systems migrated to more robust architectures long ago.

S
Sarah Jenkins23 Oct

As a freelance web developer, I have spent the last forty-eight hours doing nothing but patching servers. It is exhausting work, yet vital to ensure that my clients' data remains protected from these automated exploits.

A
Arthur Penhaligon23 Oct

It is absolutely staggering how much of the modern web relies on such fragile foundations. We have been sleepwalking into this digital crisis for years, prioritising speed of development over fundamental security protocols.

D
David O'Reilly23 Oct

People have been warning about the PHP codebase for over a decade now. It is a shame it has taken a global crisis for businesses to finally take their technical debt seriously.

M
Margaret Thorne23 Oct

I must admit, I find it quite ironic that the very technology hailed as the future of efficiency is now being used to dismantle the structures that make the internet usable. Perhaps it is time we reconsidered our dependence on these ubiquitous server-side languages.

J
James Sterling23 Oct

While the scale is concerning, let us not panic just yet. The security community is responding rapidly, and this is exactly why we need robust, long-term support for open source projects rather than just relying on unpaid volunteers.

S
Sarah Jenkins23 Oct

I work in local IT support and it has been a nightmare trying to patch our client systems this morning. Does anyone honestly believe these AI tools are going to make our infrastructure safer when they are clearly being used to weaponise simple coding errors?

A
Arthur Penhaligon23 Oct

It is absolutely staggering how much of the modern web relies on such fragile foundations. We have spent years rushing to automate everything without ever stopping to consider the systemic risks of these legacy frameworks.
More from Technology

Most Read in Technology

Morning Briefing

The day's top stories, before 7am

Join 40,000 readers who start their morning with National Post UK.