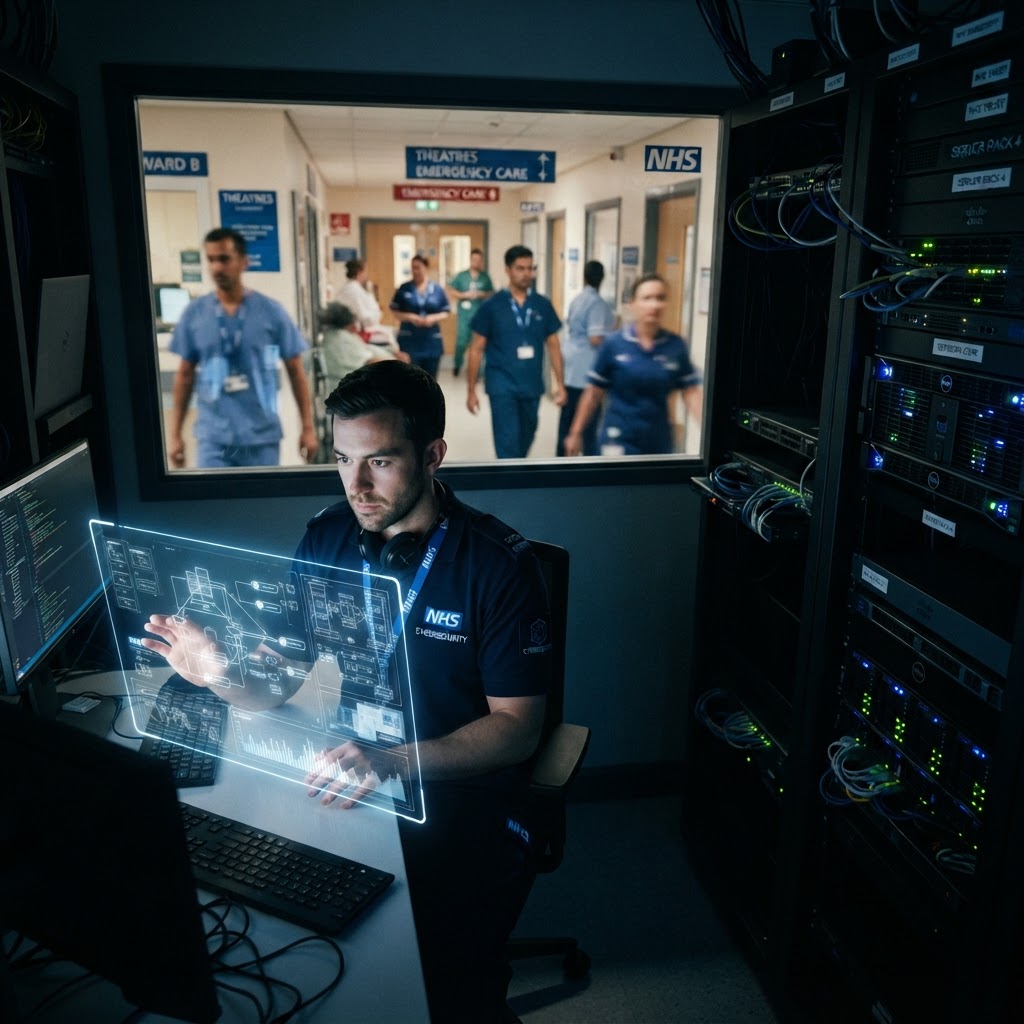
The Price of Progress The National Health Service is currently undertaking its most ambitious digital overhaul since its inception, a 10-year strategic roadmap designed to modernise patient care through the lens of artificial intelligence and Electronic Patient Records (EPR). While the promise of faster diagnostics and seamless data sharing between trusts is tangible, this rapid acceleration has placed a profound spotlight on the frailty of our digital underpinnings. As the health service becomes increasingly tethered to the cloud, the distinction between operational efficiency and cyber security has effectively evaporated.
The New Reality of Digital Dependency For the modern clinician, a functioning digital interface is no longer an optional utility but a foundational requirement for patient safety. When hospital systems falter, the impact is felt instantly in operating theatres, pharmacy departments, and oncology units across the country. Recent industry analysis confirms the severity of the climate, with 44 per cent of NHS organisations categorising cyber security risks as a pre-eminent operational challenge. This is not merely a technical concern for IT departments; it is a clinical risk that demands the same scrutiny as hospital-acquired infections or surgical errors.
Dr. Eleanor Vance, a senior fellow at the Health Foundation, notes that the shift toward integrated systems requires a parallel evolution in organisational culture. Whilst the NHS has historically prioritised perimeter defence, the focus must shift toward architectural resilience—the ability for a trust to remain functional in a degraded state. The objective is no longer the pursuit of an impenetrable wall, but the cultivation of a system that can withstand, contain, and recover from malicious interference without catastrophic loss of life or data integrity.
Legislative Guardrails The legislative landscape is poised to reflect this new reality. The forthcoming Cyber Security and Resilience Bill is widely viewed as a pivotal mechanism for institutionalising these defences. By codifying standards for digital procurement and mandatory recovery protocols, the government aims to establish a baseline of security across all Integrated Care Boards. This legislative move signals a departure from the fragmented approaches of the past, seeking instead to unify the NHS under a robust, national security umbrella that acknowledges the health service as critical national infrastructure.
Beyond Prevention: The Recovery Mandate The traditional doctrine of cyber defence has long been defined by prevention. However, in the context of the NHS, prevention is insufficient. As threats from state-aligned actors and sophisticated ransomware syndicates become more pervasive, the reality of a breach must be treated as a matter of 'when' rather than 'if'. Therefore, the priority is shifting toward business continuity. If a patient record system is encrypted by a malicious actor, how does the hospital ensure that urgent cardiac surgery proceeds without interruption? The answer lies in offline contingencies, local server mirroring, and the rigorous training of clinical staff to operate without the digital crutch.
As we head into the winter months, the pressure on the NHS to deliver on its digital transformation goals is intensifying. Yet, this ambition must be tempered by the cold reality of the threat environment. The transformation is not just about adopting AI; it is about ensuring that the architecture we build can survive the pressures of a digitised age. Failure to master this balance will not only undermine the taxpayer-funded investment in technology but will jeopardise the very essence of the service: the delivery of safe, reliable care.